Compliance,
built like product.

spektr is mission control for regulated businesses. Compliance can set the rules, Product builds the flows and Operations runs them at scale.

4.9

Get Product, Operations and Compliance in the same room

spektr aligns all three around the same workflows, information and decision. One shared system for building, launching and scaling.

Product: Build without limits
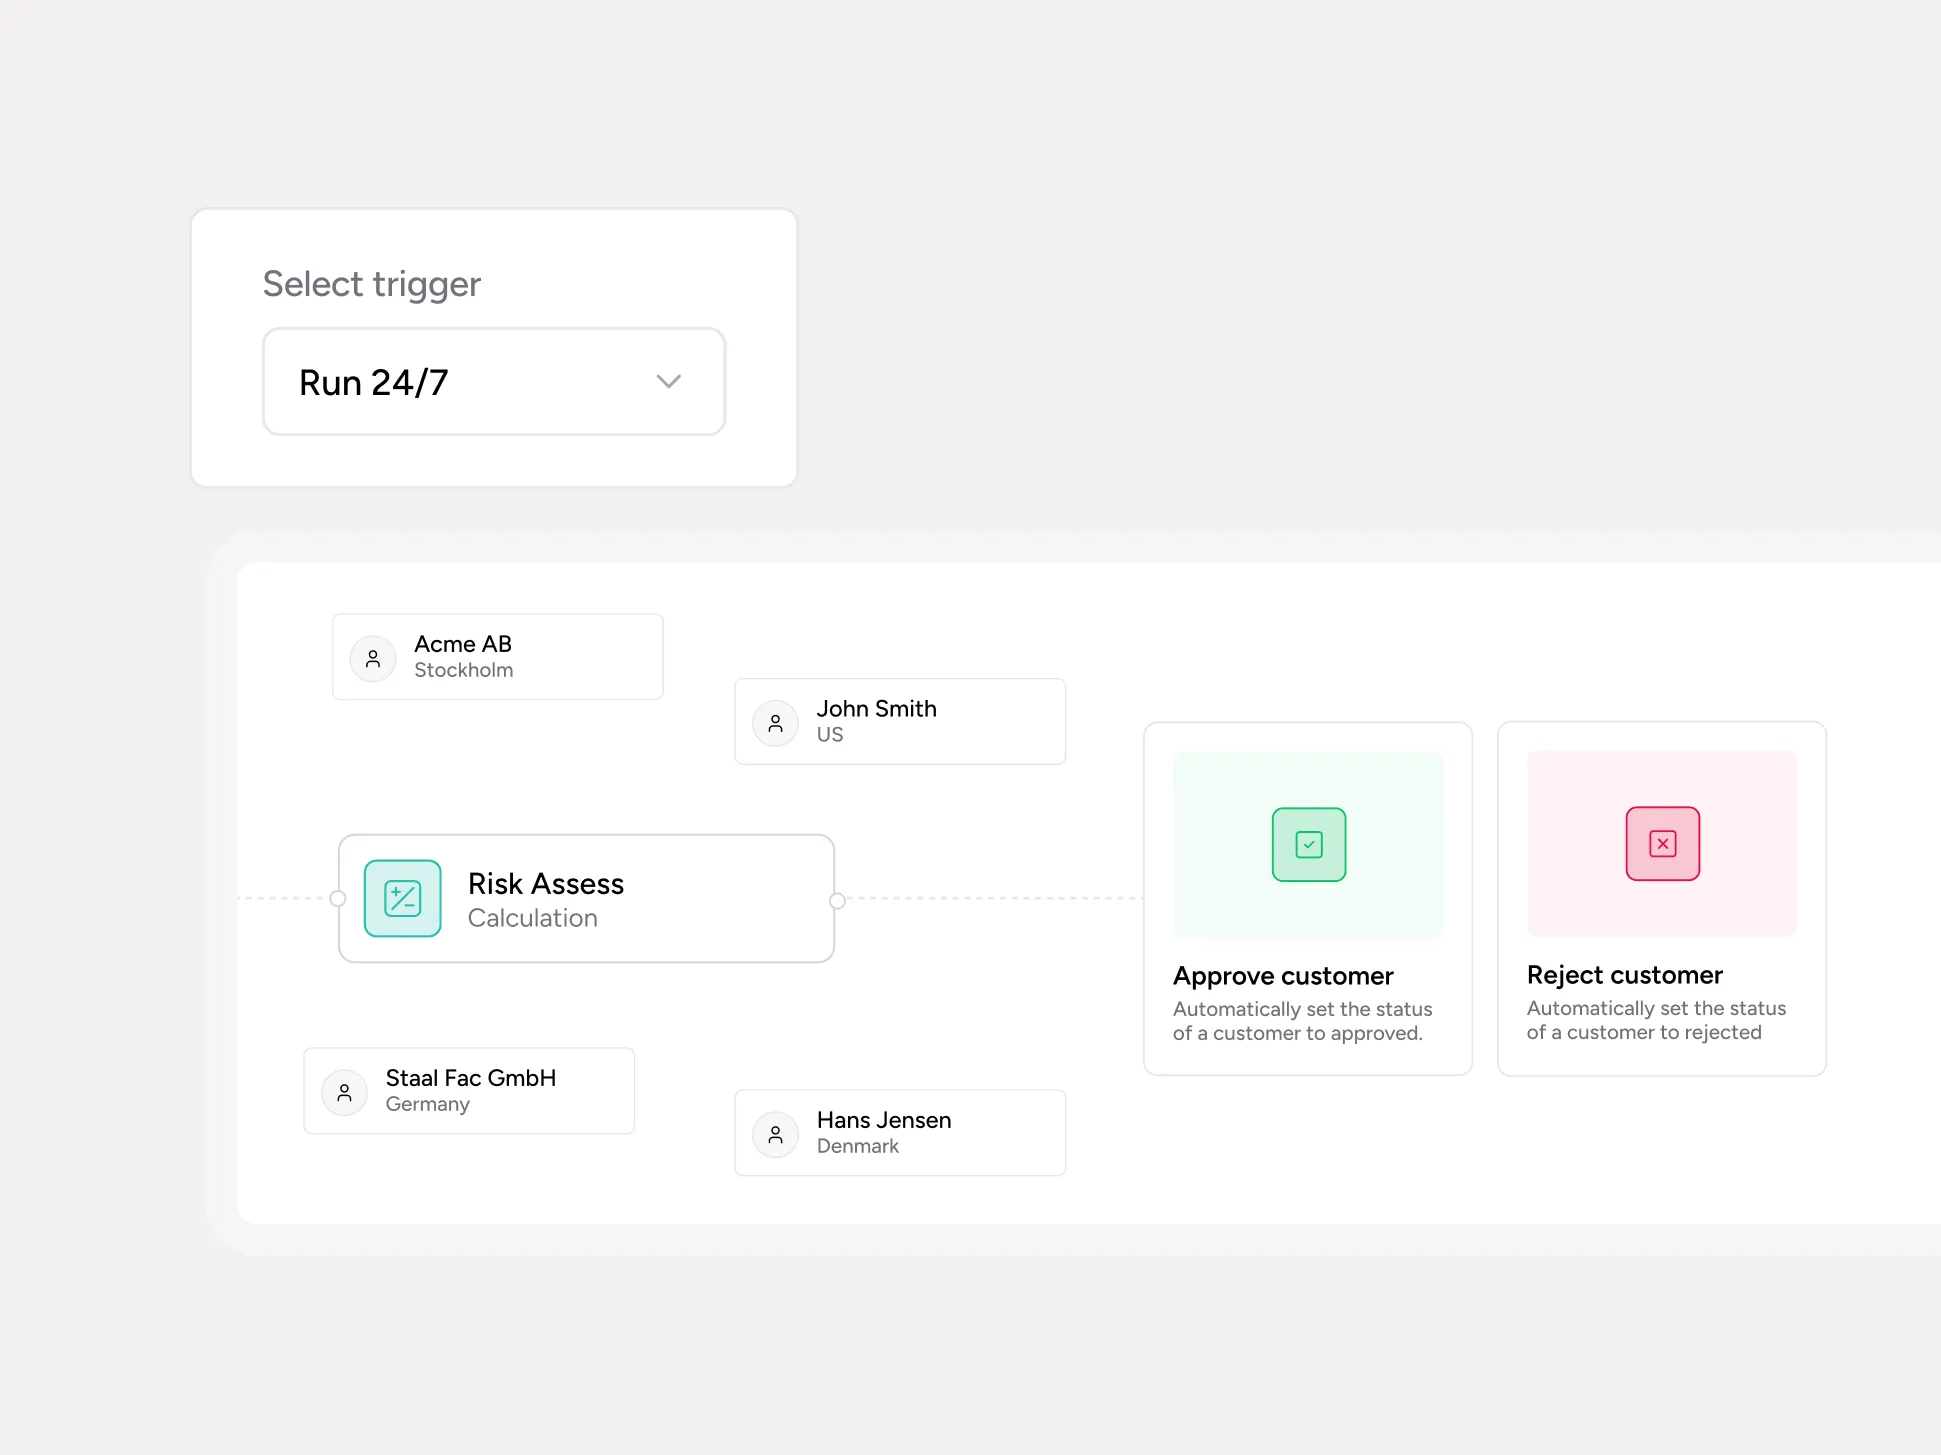
Workflows, rules and reviews are configurable by the teams who own them, so compliance becomes as buildable as product. Change a flow, open a market, launch a feature: no sprint, no backlog ticket.

Operations: Let agents help run your mission at scale
AI agents run the manual work: gathering evidence, resolving routine events and preparing cases for review. Your team stays on what's mission-critical, the decisions that need human judgement.

Compliance: Control all processes and agents using your policies
People, workflows and AI agents all write to the same traceable record, capturing every action, approval and piece of evidence. Your own policies govern what every process and agent may do, so the whole system stays ready for inspection when it counts.
"We need an infrastructure that can automate the routine work without losing the configurability each jurisdiction demands, whilst meeting increasingly complex regulatory demands."
Read case study
Mark Nelson
Head of Financial Crime Controls, at Nets Denmark
"We weren't looking for a platform that would force us to rebuild around it. We needed something that could plug into how we already operate and remove friction where it actually lives."
Read case study
Roshni Bharadwaj
Group Product Manager at Pleo
“spektr turned our most complex processes into a flow anyone can follow - bringing structure and scalability to something that used to rely heavily on internal know-how.”
Read case study
André Guardado
Head of Legal and Compliance at Santander Leasing

Enterprise-grade security and controls

spektr is built for regulated businesses and audited like one. Certified for information security, privacy and responsible AI management, SOC 2 Type II attested, and GDPR compliant.
More about security
ISO 27001:2022
Rigorous information security, safeguarding data integrity and confidentiality.
ISO 27701:2019
Independently verified privacy management compliance.
ISO/IEC 42001:2023
Responsible, ethical, and transparent AI management.
SOC 2 Type II
Independently audited security controls protecting customer data.
GDPR Compliant
All data hosted and handled within the EU.

Ready for liftoff?

Give Product, Operations and Compliance one shared system for regulated progress.